Network segmentation · Firewall engineering & automation
Engineering access controls the team can maintain.
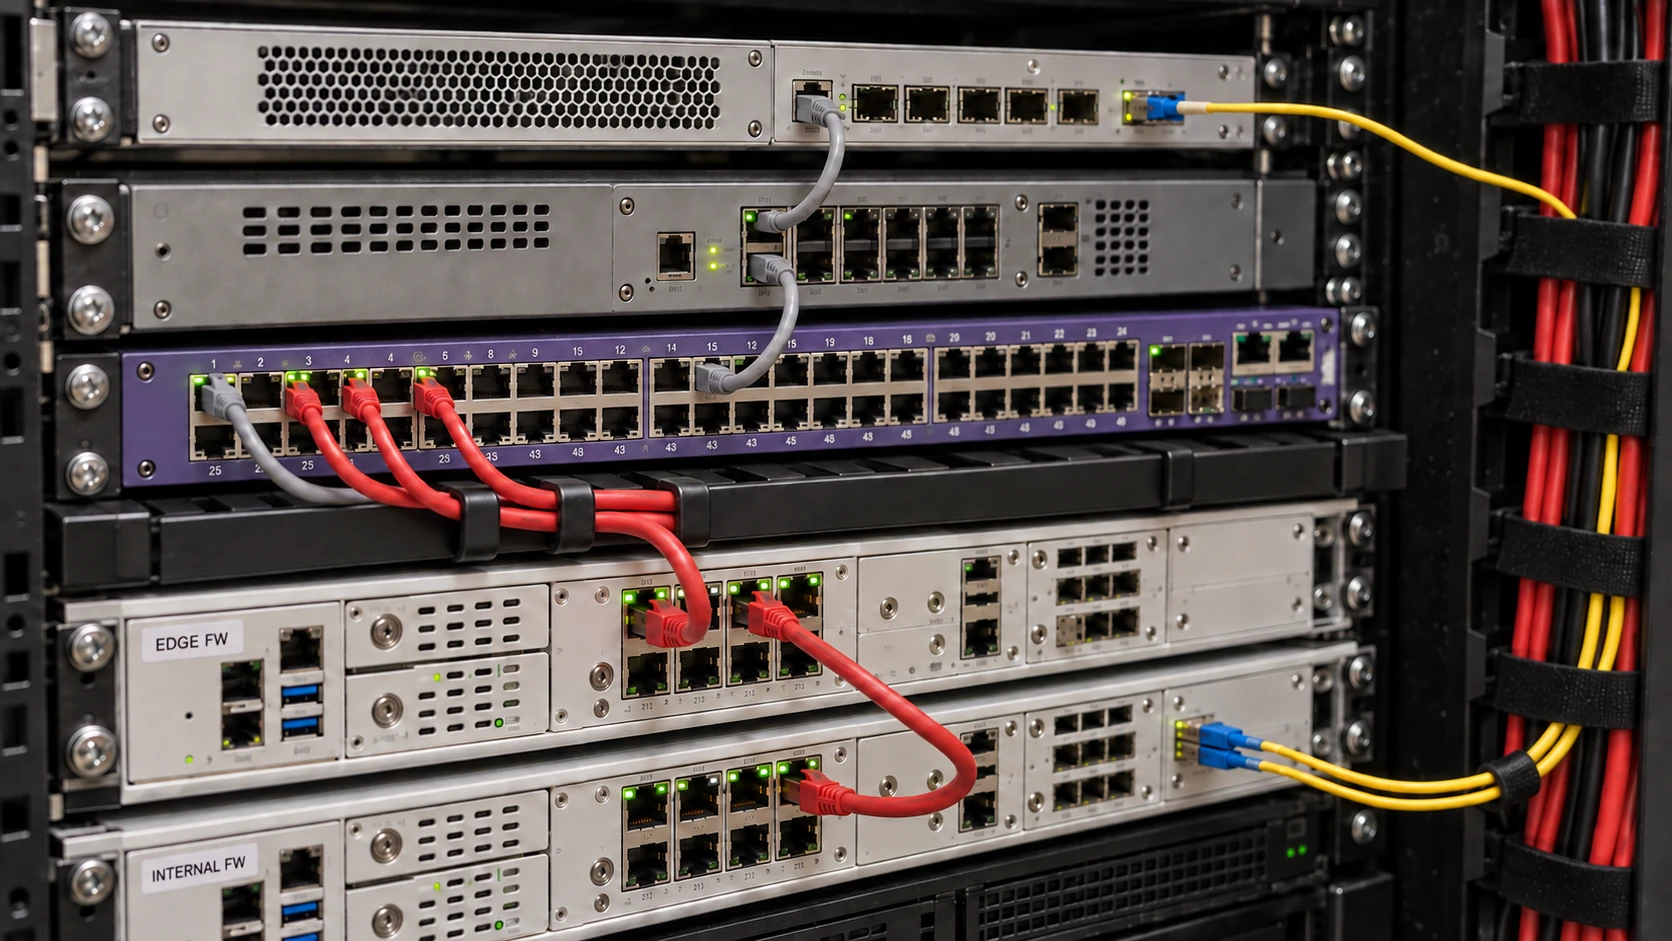
I worked with specialist suppliers on firewall deployment and segmentation, then refined policies through traffic analysis. I also developed PowerShell security tooling and trained colleagues to investigate faults and manage changes.
Translate service dependencies into security zones
I reviewed how services communicated and identified traffic groupings for meaningful firewall zones, working with specialist suppliers on implementation and the operational impact of changes.
I configured interfaces, IPv4 policies, address objects and groups, and intrusion-prevention settings. My work also included failover planning and testing.
Use traffic logs to tighten and correct policy
I analysed traffic logs to identify a connection’s source, destination, service and policy. This helped distinguish intended restrictions from rules blocking required traffic.
I used that evidence to tighten access and correct policies, then checked the affected service and explained the reason for the change.
Teach the investigation and the change process
I ran practical sessions on analysing logs, tracing connections and identifying firewall policies. I created knowledge-base articles and authored the team’s firewall change process.
I also wrote a VLAN implementation guide linking planning and network records to switching, firewall policy and access requirements. It covered connectivity and access testing, documentation and closure.
Automate recurring switch-security administration
I built a PowerShell and SSH toolkit for switch port and access-control-list (ACL) administration. It reports current port and ACL state and guides technicians through configuring or clearing controls when equipment is installed or removed.
The toolkit shows planned changes, offers a dry-run mode and requests confirmation before applying them. It accounts for existing configuration and checks command failures so the intended action and its result can be reviewed.
The result
More deliberate access. Better diagnosis.
The installed firewall controls were refined using traffic evidence, with documented firewall and VLAN change processes for ongoing administration.
I shared the switch-security toolkit with a colleague to support security administration when installing or removing equipment.